PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately.
Who is at risk: all PHP installations serving web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. We consider the risk highest for mod_php, with a demonstrated exploit where an unauthenticated request can trigger the attack before any application code runs.
The vulnerabilities:
RCE via OOM corruption, CVE-2026-109618 (GHSA-w8hw-w9fx-j79w): out-of-memory handling can interrupt PHP while internal request data is only partially initialized. Request cleanup may then treat the invalid data as valid.
RCE via stale global state, CVE-2026-109619 (GHSA-6wmf-4rv5-p3rp): request-owned internal state can survive after its backing memory has been freed. A later request handled by the same worker may use that stale state before normal initialization resets it.
Other Information
Hello,
Does InfinityFree updates php for everyone when there is a CVE (PHP: News Archive - 2026), or do we have to update it ourselves ? If yes, how so please ?
Beep boop, I’m a bot! I dug through the forum to get you started. I sometimes get things wrong though, so do with this what you will until a human has a look.
I couldn’t find anything in the knowledge base or on the forum that says whether InfinityFree updates PHP when a CVE like this comes out, or whether users can update it themselves. So I can’t tell you which it is, and I don’t want to guess about how our servers are patched.
If you want to check where your own site stands, create a PHP file containing <?php echo phpversion(); and open it in your browser. Which version does it print? That’s the version your account is running right now, and it’s the number to compare against the fixed releases in the advisory.
I ran a quick check. The 8.4.27 is a patched version of PHP - however this feature still enabled and is recommended to be turned off. I am wondering if this is a decision made to leave on or will this be turned off?
Upgrading to PHP 8.4.27 is enough to block the PHP2Shell attack, and it is the only way to fully fix it.
session.upload_progress.enabled only blocks known paths of CVE-2026-109619, and 618 remains vulnerable. Even for 619, there will be new exploit variants being discovered that makes this stopgap effectively useless.
Disabling this will make file upload progress (like image upload) on your website be completely missing, which hurt user’s experience while providing minimal effectiveness.
Just for your peace of mind, yes, it is left on intentionally, the vulnerability is fully patched as per iFastNet’s support page:
There is no in your opinion. The ONLY way to patch it is by updating PHP, either to an officially fixed version or a backport. (I doubt you tested it yourself with a PoC)
Blocking multipart blocks some attacker paths, but not all. Your other two rules do absolutely nothing and may hinder UX.
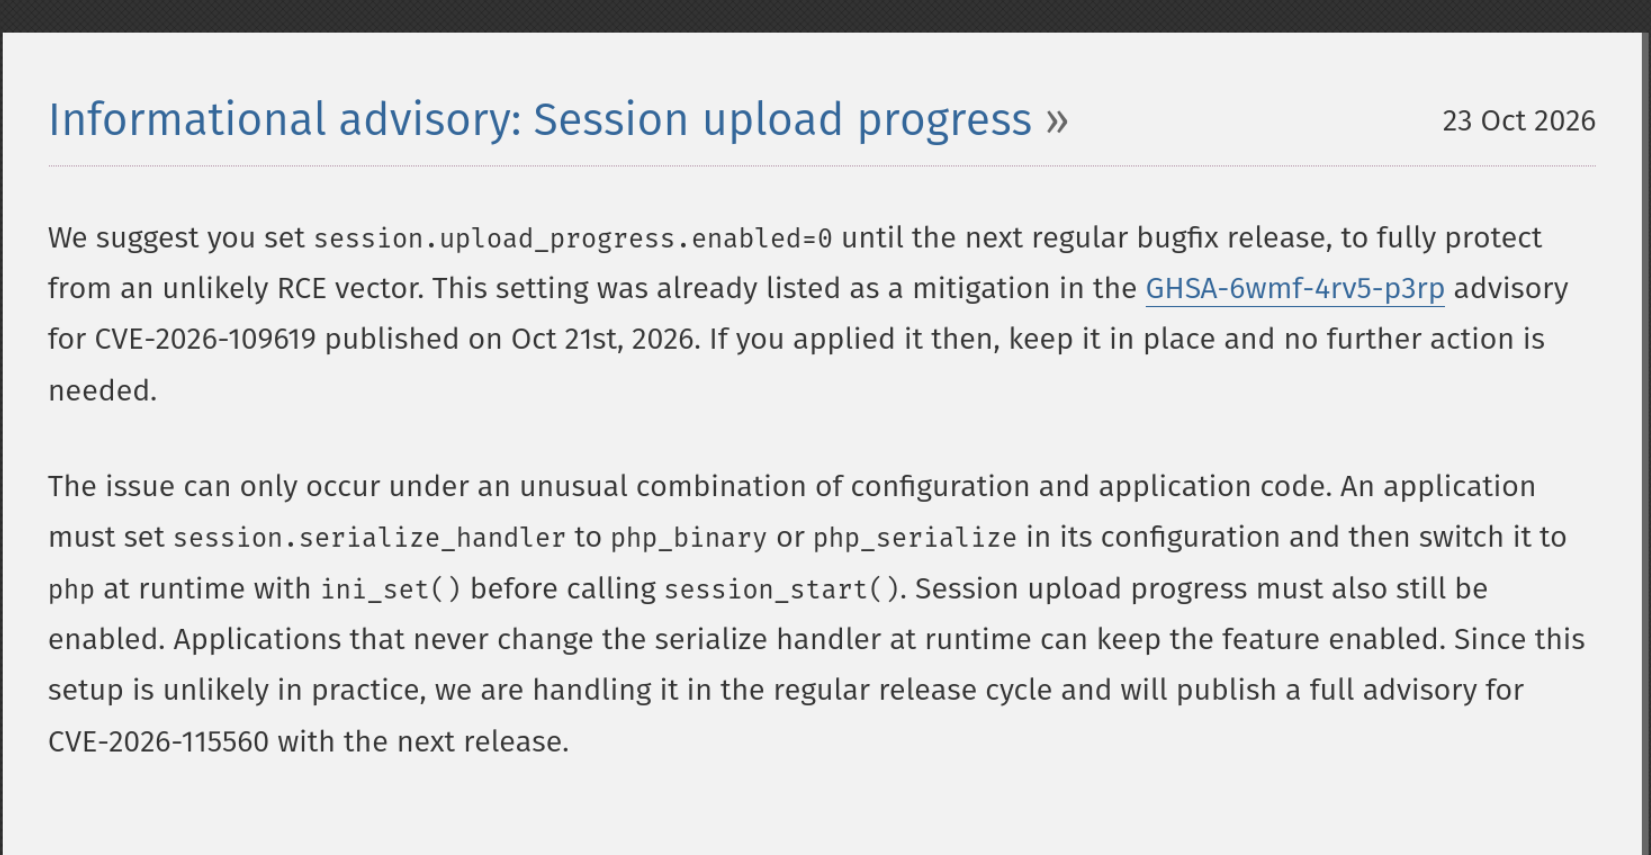
About this though, PHP now recommends upload progress disabled in PHP ini even if on a patched version: Note that this must be set via php ini, not even in individual PHP files, so the WAF rule above blocking it still does pretty much nothing.
Do note that this is an another (3rd) CVE, the patches on Wednesday are doing is job, but there is a new RCE vulnerability circulating, and this is the one.
However, you need to oddly override session.serialize_handler specifically at runtime for this exploit to work so it’s practically unlikely to happen, thus deferred the patch to standard bugfix version.
Edit: I do not believe free hosting is affected by this new CVE
You see ? That’s another bug in upload_progress in php 8.4.27 (the update patch for PHP2Shell) and this is my firewall rule → any(http.request.headers[“content-type”][*] contains “multipart/form-data”) and (http.request.uri.query contains “PHP_SESSION_UPLOAD_PROGRESS” or http.request.uri.path contains “PHP_”). If you don’t have WAF you should Set session.upload_progress.enabled = 0 in php.ini or the PHP-FPM pool, then restart PHP-FPM.
If you meant the “Informational advisory CVE-2026-109619” that I already mentioned in my previous message, I am confident that free hosting is not vulnerable from the start, and that upload progress = 0 config ini is not needed.
An application must set session.serialize_handler to php_binary or php_serialize in its configuration and then switch it to php at runtime with ini_set() before calling session_start()
On free hosting the serialize handler in the config is php, and not php_serialize/binary. so it’s not vulnerable.
You are just hurting your visitor’s UX by disabling it in WAF.
But since you don’t care, good luck getting complaints from your visitors.