Hi,
I install successfully from softaculous open source point of sale however when i go to the url, i keep getting error msg = “Something went wrong”
There are some instrucction to follow but they don’t apply since it is a fresh installation.
Could you please help me to resolve this issue.
Other Information
Something Went Wrong!
Our apologies, but the website has encountered an error and cannot display this page at the moment.
The issue is likely due to a code error within the .htaccess file, which controls important server configurations. This error is not related to any PHP files or other website code.
Welcome to the InfinityFree community forum! Good to have you here.
Most people answering here are volunteers. They’re often the fastest source of help. Admin (the only staff member) checks in about once a day for issues on our end.
Volunteers can’t see your account or website. Share what you actually see, like error messages and what happens when you try something. That’s more useful than your theory of what’s wrong.
AI tools often get InfinityFree wrong. If a volunteer’s advice differs from what an AI told you, please try the volunteer’s suggestion first.
Solving an issue is a joint effort. Try the suggestions you get and report back what happened.
Beep boop, I’m a bot! I dug through the forum to get you started. I sometimes get things wrong though, so do with this what you will until a human has a look.
That “Something Went Wrong!” page means one of the .htaccess files on the path to your page has a line the server can’t accept. It doesn’t matter that the install is fresh. The cause is the .htaccess file, not your PHP code, and the installer’s own file can be the one with the problem. This knowledge base article covers it:
The server reads the .htaccess in the folder of the page you open and in every folder above it, up to htdocs. For your URL that means htdocs/pos/public, htdocs/pos and htdocs itself. Any of them can cause the error.
To find which one, rename each of those .htaccess files in turn (for example to .htaccess.bak) and reload the page. When the error goes away, you’ve found the file.
Could you paste the contents of that file here? Then someone can see which line the server is rejecting.
# redirect to public page
<IfModule mod_rewrite.c>
    RewriteEngine On
    RewriteCond %{REQUEST_URI} !^public$
    RewriteCond %{REQUEST_URI} !^/.well-known/acme-challenge [NC]
    #RewriteRule "^(.*)$" "/public/" [R=301,L]
    # If you installed CodeIgniter in a subfolder, you will need to
    # change the following line to match the subfolder you need. Uncomment
    # the line below and comment the line above.
    RewriteRule "^(.*)$"  "/pos/public/" [R=301,L]
</IfModule>
	# disable directory browsing
	# For security reasons, Option all cannot be overridden.
Options +SymLinksIfOwnerMatch -Indexes
	# prevent folder listing
IndexIgnore *
<IfModule mod_headers.c>
  Header always set X-Frame-Options "SAMEORIGIN"
</Ifmodule>
<IfModule authz_core_module>
  # secure htaccess file
  <Files .htaccess>
    Require all denied
  </Files>
  # prevent access to PHP error log
  <Files error_log>
    Require all denied
  </Files>
  # prevent access to LICENSE
  <Files LICENSE>
    Require all denied
  </Files>
  # prevent access to csv, txt and md files
  <FilesMatch "\.(csv|txt|md|yml|json|lock|env)$">
    Require all denied
  </FilesMatch>
</IfModule>
Under pos\public .htaccess content is shared below:
# Disable directory browsing
Options All -Indexes

# ----------------------------------------------------------------------
# Rewrite engine
# ----------------------------------------------------------------------

# Turning on the rewrite engine is necessary for the following rules and features.
# FollowSymLinks must be enabled for this to work.
<IfModule mod_rewrite.c>
    Options +SymLinksIfOwnerMatch
    RewriteEngine On

    # If you installed CodeIgniter in a subfolder, you will need to
    # change the following line to match the subfolder you need.
    # http://httpd.apache.org/docs/current/mod/mod_rewrite.html#rewritebase
    # RewriteBase /

    # Redirect Trailing Slashes...
    # RewriteCond %{REQUEST_FILENAME} !-d
    # RewriteCond %{REQUEST_URI} (.+)/$
    # RewriteRule ^ %1 [L,R=301]

    # Rewrite "www.example.com -> example.com"
    RewriteCond %{HTTPS} !=on
    RewriteCond %{HTTP_HOST} ^www\.(.+)$ [NC]
    RewriteRule ^ http://%1%{REQUEST_URI} [R=301,L]

    # To redirect a subdomain to a subdir because of https not supporting wildcards
    # replace values between <> with your values
    # RewriteCond %{HTTP_HOST} ^<OSPOS subdomain>\.<my web domain>\.com$ [OR]
    # RewriteCond %{HTTP_HOST} ^www\.<OSPOS subdomain>\.<my web domain>\.com$
    # RewriteRule ^/?$ "https\:\/\/www\.<my web domain>\.com\/<OSPOS path>" [R=301,L]

    # Checks to see if the user is attempting to access a valid file,
    # such as an image or css document, if this isn't true it sends the
    # request to the front controller, index.php
    RewriteCond %{REQUEST_FILENAME} !-f
    RewriteCond %{REQUEST_FILENAME} !-d

    # If in web root
    RewriteRule ^([\s\S]*)$ index.php/$1 [L,NC,QSA]

    # If in subdir comment above line, uncomment the line below and replace <PATH> with your path
    #RewriteRule ^(.*)$ /<PATH>/public/index.php?/$1 [L]

    # Ensure Authorization header is passed along
    RewriteCond %{HTTP:Authorization} .
    RewriteRule .* - [E=HTTP_AUTHORIZATION:%{HTTP:Authorization}]
</IfModule>
<IfModule !mod_rewrite.c>
    # If we don't have mod_rewrite installed, all 404's
    # can be sent to index.php, and everything works as normal.
    ErrorDocument 404 index.php
</IfModule>
	# Disable server signature start
	ServerSignature Off
	# Disable server signature end
<IfModule mod_expires.c>
  <FilesMatch "\.(jpe?g|png|gif|js|css)$">
    ExpiresActive On
    ExpiresDefault "access plus 1 week"
  </FilesMatch>
</IfModule>
<IfModule mod_headers.c>
  Header always set X-Frame-Options "SAMEORIGIN"
  Header add Content-Security-Policy "default-src 'self' www.google.com; connect-src 'self' nominatim.openstreetmap.org; script-src 'self' 'unsafe-inline' 'unsafe-eval' www.google.com www.gstatic.com; style-src 'self' 'unsafe-inline' fonts.googleapis.com; font-src 'self' fonts.googleapis.com fonts.gstatic.com; img-src 'self' data: blob:; object-src 'none'; form-action 'self'"
  Header set X-Content-Type-Options "nosniff"
  Header set X-XSS-Protection "1; mode=block"
  Header set X-Frame-Options "DENY"
</Ifmodule>
	# prevent folder listing
	IndexIgnore *
<IfModule authz_core_module>
  # secure htaccess file
  <Files .htaccess>
    Require all denied
  </Files>
  # prevent access to PHP error log
  <Files error_log>
    Require all denied
  </Files>
</IfModule>
Could you please share your .htaccess file again? And this time, please make sure to wrap it in a code block, don’t just paste it into the composer field. Without a code block, the composer will try to parse your input and end up mangling it and breaking your code anyway, which makes it harder for us to check what’s wrong.
Ah, I see the issue, and it’s very simple to fix. The problem is this line:
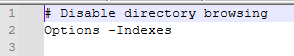
To fix it, replace it with this:
Options -Indexes
Ironically, your own code actually already says why that is:
That’s in the other .htaccess file, which does set this correctly.
We recently made some improvements to the security of our hosting, which included disabling some unnecessary .htaccess functionality. It doesn’t cause any changes in functionality, but it did make it so that .htaccess rules that previously just didn’t do anything would now actually break.
Looking at the entirety of the .htaccess files a bit more closely, there are a quite a few things in it which look “off” to me: probably unnecessary, and potentially not supported.
Could you please try and remove all the .htaccess code except for rewrite rules and see if that allows your site to work?
If it does, you can then add the security related rules back one by one to try and find out which is causing the issue.
But quite a few of them do nothing. Just to name a few:
Directory listing is disabled by default on our hosting.
.htaccess files cannot be downloaded (no sane sysadmin would allow that, and I’m pretty sure that servers that support .htaccess rules won’t even let you).
Cross origin requests, whether other website embed your site, are blocked on our hosting.