# Domain serving injected “/aes.js” + “\_\_test” challenge (OpenResty) — Google flagged as deceptive sit
**URL:** https://forum.infinityfree.com/t/domain-serving-injected-aes-js-test-challenge-openresty-google-flagged-as-deceptive-sit/117317
**Category:** Hosting Support
**Created:** [January 22, 2026, 2:33pm UTC](https://forum.infinityfree.com/t/domain-serving-injected-aes-js-test-challenge-openresty-google-flagged-as-deceptive-sit/117317 "2026-01-22T14:33:08Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@Giomar.marchisio](https://forum.infinityfree.com/u/Giomar.marchisio)
#### Post date: [January 22, 2026, 2:33pm UTC](https://forum.infinityfree.com/t/domain-serving-injected-aes-js-test-challenge-openresty-google-flagged-as-deceptive-sit/117317/1 "2026-01-22T14:33:08Z")
### Hello InfinityFree team,
My domain **[gestionmarchi.com](http://gestionmarchi.com)** has been flagged by Google as a _deceptive site / social engineering_, and I’m trying to remove the cause so I can request a successful review.
### What is happening
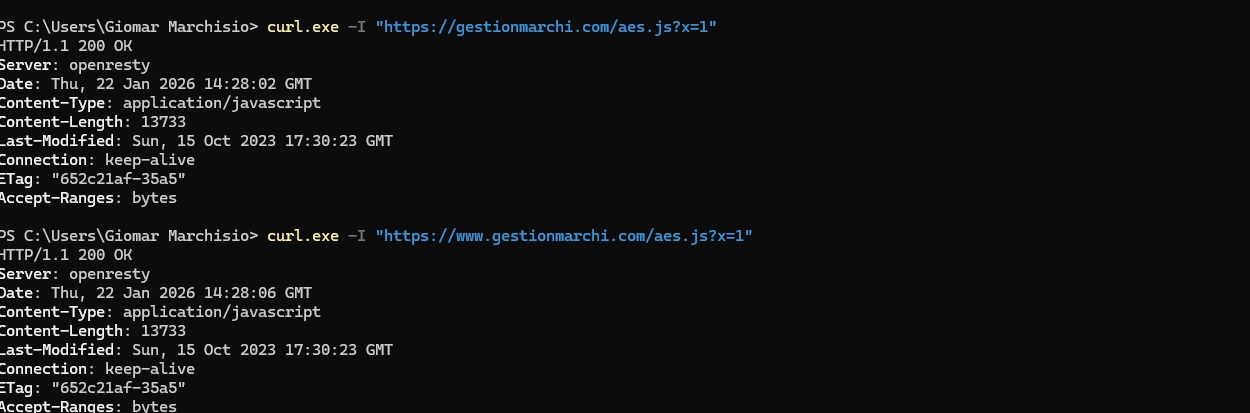
When I request the homepage directly from the origin server (without Cloudflare proxy), the server returns an **HTML/JS challenge** that loads `/aes.js`, sets a cookie called `__test`, and redirects to `/?i=1`. The response header shows **Server: openresty**.
This content is **NOT part of my website project** (I searched my project files and there is no `aes.js`, `slowAES`, `__test`, `toNumbers`, etc.). It looks like an injection or server-level rule.
Evidence (curl output)
**HTTP (port 80)**
HTTP/1.1 200 OK
Server: openresty
Content-Type: text/html
HTTPS (port 443)
curl.exe -vk --http1.1 -A “Mozilla/5.0” “[https://gestionmarchi.com/”](https://gestionmarchi.com/%E2%80%9D)
HTTP/1.1 200 OK
Server: openresty
Content-Type: text/html
Also, requesting `/__test` returns Cloudflare-style errors (520) when proxied, and origin responses are inconsistent, which made me suspect proxy/origin security behavior.
### What I already tried
1. I checked my website files and **`aes.js` does not exist in my project**.
2. I downloaded the full account files as a ZIP and searched for:
3. Cloudflare was previously **Proxied** and returned **520** ; I switched DNS records to **DNS only** (grey cloud) to troubleshoot origin directly.
### Request / What I need help with
Could you please:
1. Confirm if InfinityFree adds any **OpenResty/Nginx security challenge** that injects `/aes.js` + `__test` cookie, and if so, how can it be disabled for my domain?
2. If this is NOT expected behavior, can you check whether my hosting account or domain is affected by:
3. Provide the exact steps I should follow to fully clean this so Google Safe Browsing review will pass.
I’m happy to provide any additional info you need (account username, hosting details, etc.).
Thank you for your help — this is urgent because the domain reputation is impacted.
Best regards,
**Giomar Marchisio**
---
### Author:  [@dan3008](https://forum.infinityfree.com/u/dan3008)
#### Post date: [January 22, 2026, 2:42pm UTC](https://forum.infinityfree.com/t/domain-serving-injected-aes-js-test-challenge-openresty-google-flagged-as-deceptive-sit/117317/2 "2026-01-22T14:42:26Z")
> [@Giomar.marchisio](#):
>
> Confirm if InfinityFree adds any **OpenResty/Nginx security challenge** that injects `/aes.js` + `__test` cookie, and if so, how can it be disabled for my domain?
This is part of the security system. This helps explain it further:
> [@Why do I see ?i=1 at the end of a URL](https://forum.infinityfree.com/t/why-do-i-see-i-1-at-the-end-of-a-url/49356):
>
> Don’t worry, this is normal! When you visit your website, you might notice ?i=1 added to the end of your URL. Here’s what’s happening and why. What is the ?i=1 suffix? The ?i=1 is a security check that protects your website from bots and malicious traffic. Our system needs to verify you’re using a real web browser before letting you access your site. Why does it appear? When you first visit your website, our security system: Sends a small test to your browser Checks if your browser can store…
That said, this shouldn’t trigger the deceptive site warning from google safe search
The more likely reason this is showing is because your sites home page is a fairly generic login page, with no details as to what the site is or what you’re logging into.
I’d recommend adding a landing page with some details about your site, that then links to a login page. I know it seems excessive, but there’s a reason most sites you visit online don’t have their homepage as just a “log in” page
This article may help you too:
> [@Why Do I See a "Deceptive Site Ahead" Warning on My Website?](https://forum.infinityfree.com/t/why-do-i-see-a-deceptive-site-ahead-warning-on-my-website/99495):
>
> If you’re trying to access your website and encounter a bright red warning page that looks something like this: Deceptive site ahead Firefox blocked this page because it may trick you into doing something dangerous like installing software or revealing personal information such as passwords or credit cards. Advisory provided by [Google Safe Browsing](https://developers.google.com/safe-browsing/v4/advisory). Don’t worry - you’re not alone. This article will explain what this warning means, why it appears, and what steps you can take to fix it. What…
---
### Author:  [@system](https://forum.infinityfree.com/u/system)
#### Post date: [January 29, 2026, 2:43pm UTC](https://forum.infinityfree.com/t/domain-serving-injected-aes-js-test-challenge-openresty-google-flagged-as-deceptive-sit/117317/3 "2026-01-29T14:43:16Z")
This topic was automatically closed 7 days after the last reply. New replies are no longer allowed.